Fragmented IAM architectures have a devastating effect, even if it isn’t always obvious: they create more blind spots while consuming hours of the technical team’s time on repetitive coordination tasks that, despite the effort, never manage to cover all fronts.
According to the CrowdStrike 2026 Global Threat Report, 82% of intrusion detections were not malware-based. Behind that figure lies a reality: the security landscape is changing and putting identities in the crosshairs. In light of this, there is a growing sense that identity architecture functions as a temporary fix (even if it has been in place for years). And the cost of that makeshift architecture becomes apparent at the worst possible moment: when an incident occurs.
According to the CrowdStrike 2026 Global Threat Report, 82% of intrusion detections were not malware-based. Behind that figure lies a reality: the security landscape is changing, and identities have become one of the primary entry points for attackers.
When identity management tools are scattered and do not communicate with one another, a compromised account can move between systems without the security team having a complete view of what is happening. That is where a makeshift, patchwork architecture reveals its greatest weakness.
At Soffid, we help design unified IAM models from the ground up, capable of eliminating blind spots, connecting disparate systems, and turning complexity into control.
In light of this, building a unified and scalable IAM model offers a clear alternative: moving away from an approach that relies on retrofitting tools and, instead, adopting a convergent architecture from the outset. Here’s how.
Friction that builds up day by day. This is the result of a fragmented IAM architecture, in which each environment manages identities using different tools, and in which various applications operate without knowing what is happening in the others.
On a practical level, decentralization leads to numerous obstacles and friction points, but also to risks:
The result is a lack of control, with entry points left exposed and teams finding that identity management slows down their work.
A converged IAM architecture integrates IGA, AM, and PAM under a single core, eliminating the gaps between tools that typically operate separately.
In day-to-day operations, a unified IAM architecture involves:
Beyond day-to-day operations, a unified IAM architecture also offers significant benefits for the organization as a whole:
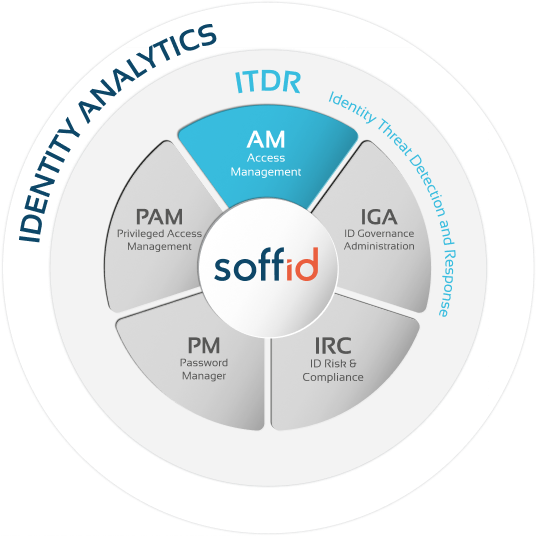
Stop jumping from one tool to another and taking unnecessary risks due to a fragmented architecture. At Soffid IAM, we turn that complexity into control: we unify your IAM architecture into a single model so you can manage identities, access, and privileges from a single point, without forced integrations or last-minute patches.
Contact us and tell us about your environment so we can explore how our solution can simplify and protect it.